2026 CCPA Update: What US Small Sites Must Do About Cookie Consent
2026 CCPA Update: What US Small Sites Must Do About Cookie Consent
Under the CCPA and CPRA, most U.S. websites operate on an opt-out model, not an opt-in one. Cookies can load without a pop-up asking permission first, but if you sell or share personal data, you must give visitors an easy way to opt out through a “Do Not Sell or Share” link, honor Global Privacy Control signals, and skip any design tricks that make opting out harder than opting in.
TL;DR:
- Most websites are legally required to honor “Do Not Sell or Share” links and Global Privacy Control signals, especially when targeting California residents.
- Cookie banners must be symmetrical, easy to understand, and free of manipulative design, with clear links to privacy choices; dark patterns trigger enforcement actions.
- Compliance depends heavily on detecting the GPC signal early and suppressing sale or sharing tags before they fire, with visible confirmation of opt-out receipt by January 2026.
- The law applies to any business with California visitors that meet revenue or data-sharing thresholds, even if the business is based outside California or outside the US.
- Proper technical setup involves server-side detection of GPC, conditional tag gating, persistent opt-out logging, and transparent privacy disclosures at collection.
Table of Contents
- Who the CCPA Cookie Consent Rules Actually Apply To
- Does CCPA Require Cookie Consent? Opt-In vs. Opt-Out Explained
- Global Privacy Control: What to Detect and How to Confirm It
- Cookie Banner Design Rules: Symmetry and Dark-Pattern Bans
- A Technical Checklist for CCPA-Compliant Cookie Handling
- What Your Privacy Policy and Notice at Collection Must Say
- Enforcement Trends: What’s Actually Getting Businesses Fined
- Implementation Notes From Moderatemurmurations for US Client Sites
- Balancing Compliance and Conversion: An Editorial Take
- Get Your Cookie Consent Flow Built Right the First Time
- Sources
Who the CCPA Cookie Consent Rules Actually Apply To
Not every website with a cookie banner needs to worry about California’s privacy law. The CCPA, as amended by the CPRA, applies to for-profit businesses that do business in California and meet at least one of three thresholds: annual gross revenue exceeding a high threshold, buying or selling personal information for many consumers or households annually, or deriving a significant portion of revenue from selling or sharing personal information.
That last threshold catches more small sites than owners expect.
Cookies matter here because of how the CCPA defines “sale” and “share.” It’s broad enough to cover a lot of routine marketing tools:
- First-party analytics (measuring your own visitors on your own site) usually does not constitute a sale.
- Third-party advertising pixels (Meta Pixel, Google Ads remarketing tags) that transmit visitor data to an ad network for cross-context targeting almost always count as sharing.
- Cross-site ID syncing, where a cookie links your visitor’s identity to a profile on another platform, is one of the clearest triggers for opt-out obligations.
- Session cookies for cart functionality or login state generally fall outside the sale/share definition entirely.
Territorial reach is not limited to companies headquartered in California. Any business meeting the thresholds above and collecting data from California residents falls under the law, regardless of where the server sits or where the company is incorporated. That means an online store based in Ohio selling nationwide still needs to honor California’s rules for its California visitors, and if a meaningful share of that traffic comes from the EU or EEA, the consent strategy has to account for GDPR’s stricter opt-in requirement at the same time.
Does CCPA Require Cookie Consent? Opt-In vs. Opt-Out Explained
The short version: CCPA does not require you to ask permission before cookies fire. That’s the single most misunderstood point in California privacy compliance, and it’s the reason so many small business sites over-build their banners based on European norms that don’t apply to them.
The FTC’s own guidance confirms that the CCPA generally functions as an opt-out regime, meaning cookies and tracking scripts can load by default. Your obligation kicks in only when that data collection qualifies as a “sale” or “share.” At that point, you need a clear opt-out mechanism, not a blocking consent wall.
There’s an important exception. For consumers the business has actual knowledge are under 16, the law flips to opt-in: you need affirmative consent before selling or sharing their data. For children under 13, that consent must come from a parent or guardian. If your site’s audience includes minors, even incidentally through a blog comment section or an email signup aimed at students, this distinction changes your entire flow.
Here’s what typically triggers sale or sharing obligations versus what usually doesn’t:
- Retargeting pixels that follow a visitor across other websites: triggers opt-out obligations.
- Cross-device or cross-site ID syncing for ad measurement: triggers opt-out obligations.
- Server-side analytics you control and never transmit externally: generally does not trigger them.
- Chat widgets or CRM tools that only store data internally: generally does not trigger them, unless that data later feeds an ad network.
Quick fact: As of January 1, 2026, businesses must show visible confirmation that a Global Privacy Control signal was recognized and acted on, under 11 CCR § 7025©(6). Silent compliance no longer counts.
For sites with meaningful EEA traffic, the practical move is a geo-targeted flow: opt-in consent banners for European visitors to satisfy GDPR, and opt-out symmetry (equal-weight accept/decline options) for California visitors. This approach, sometimes called a dual-region consent strategy, keeps your analytics running for the audience that doesn’t require a blocking gate while staying inside the law for the audience that does.
Global Privacy Control: What to Detect and How to Confirm It
Global Privacy Control, or GPC, is a browser-level signal that tells every website a visitor loads: “Don’t sell or share my data.” It’s the mechanism that turns CCPA’s opt-out right from a theoretical link buried in your footer into something a visitor can set once and carry everywhere.
Technically, GPC shows up two ways: as an HTTP request header (Sec-GPC: 1) sent with every page load, and as a JavaScript property (navigator.globalPrivacyControl) that returns true when active. Browsers and extensions including Brave, DuckDuckGo Privacy Browser, and the Privacy Badger extension ship it by default, and Firefox users can enable it through settings.
The regulatory requirement is not optional once a business sells or shares data: you must honor the signal and, as of January 2026, display a visible confirmation that you did. A quiet backend suppression of ad tags isn’t enough anymore.
- Detect the signal on every page load, either through the
Sec-GPCheader at the server level or thenavigator.globalPrivacyControlproperty client-side, whichever your CMP or hosting stack supports more reliably. - Suppress sale/sharing tags immediately once detected, before any ad pixel or cross-site syncing script has a chance to fire.
- Show a visible confirmation somewhere in the interface, a small banner or footer note stating the opt-out was recognized and applied, per the Consenteo practitioner guidance on CCPA cookie banners.
- Account for propagation gaps. GPC is set at the browser or device level, so a visitor who logs into an account on a different device won’t automatically carry the same signal unless you also honor account-level opt-out preferences.
Most CMP platforms now support GPC detection natively, but if you’re running a lightweight or custom-built site, this is exactly the kind of gap that shows up in an audit before it shows up anywhere else.
Cookie Banner Design Rules: Symmetry and Dark-Pattern Bans
California regulators care less about what your banner says than about whether both choices, accept and decline, take the same effort to find and click. That’s the “symmetry in choice” standard, and it’s the single biggest source of compliance failures for otherwise well-meaning small business sites.
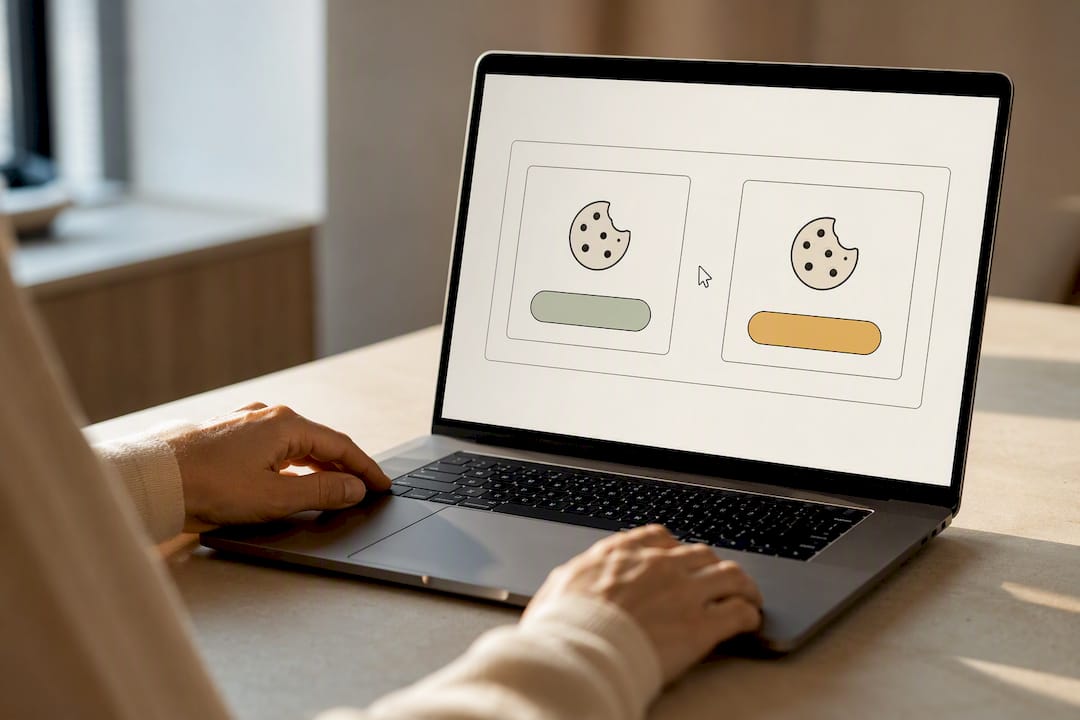
The CPPA’s Enforcement Advisory No. 2024-02 states plainly that consent obtained through dark patterns doesn’t count as valid consent at all, no matter how many visitors technically clicked “accept.” The final CCPA/CPRA implementing regulations go further, requiring that methods for exercising privacy rights be symmetrical, easy to understand, and free of confusing interactive elements.
Here’s what regulators are actively flagging as violations:
- A large, colorful “Accept All” button next to a tiny gray “Decline” link buried in fine print.
- Pre-checked opt-in boxes that require the visitor to notice and uncheck them.
- An “Ask Me Later” option that delays the choice instead of respecting it.
- Treating a visitor’s closing of the banner, or continued scrolling, as implied consent.
- Countdown timers or extra confirmation steps that appear only when a visitor tries to opt out, not when they opt in.
Regulators describe this pattern as “choice architecture” manipulation, and it’s become one of the most common enforcement triggers because it’s so easy to spot in a screenshot.
Pro Tip: Run the “squint test” on your own banner. Squint at it from across the room. If you can immediately spot the accept button but have to search for decline, redesign it, because a regulator running the same test will spot the same problem.
On required link wording: the CPPA’s general notices guidance and industry compliance guides confirm you need either a “Do Not Sell or Share My Personal Information” link, or the simpler single-link alternative, “Your Privacy Choices” paired with the official blue toggle icon. Either version must sit somewhere conspicuous, typically the footer, on every page that collects personal information. Burying it three clicks deep in a settings menu defeats the point and invites scrutiny.
If you want a plain-language model of how a small site handles this without over-engineering it, the cookie policy Jay Scott Coaching publishes is a reasonable reference point for tone and structure.
A Technical Checklist for CCPA-Compliant Cookie Handling
Getting the legal requirements right on paper means nothing if your tag manager fires ad pixels before your banner even finishes rendering. Compliance here is as much a development task as a legal one.
- Detect GPC before any tags fire. Check the
Sec-GPCheader server-side, ornavigator.globalPrivacyControlclient-side, at the earliest point in your page load, ideally before your tag manager container initializes. - Gate sale/sharing tags behind that detection. Google Tag Manager, or whatever tag manager you’re running, needs conditional triggers that block retargeting pixels and cross-site sync scripts the moment GPC or a manual opt-out is present.
- Decide server-side vs. client-side responsibility. A consent management platform (CMP) typically handles the visible banner and stores the preference, but the actual tag suppression should happen server-side wherever possible, since client-side blocking can be bypassed by ad blockers that misfire or scripts that load out of order.
- Log every opt-out event with a timestamp, so you have a record if a regulator or a consumer disputes whether their preference was honored.
- Build the visible confirmation UI required under § 7025©(6), a small, persistent indicator that the opt-out was received and applied.
- Test across browsers, since GPC support varies. Confirm behavior in Brave and DuckDuckGo, where it’s on by default, and in Firefox, where users must enable it manually.
| Component | Handles | Typical owner |
|---|---|---|
| Consent banner UI | Displaying symmetrical accept/decline choices | CMP or front-end developer |
| GPC detection | Reading Sec-GPC header or JS property |
Server or front-end developer |
| Tag gating | Blocking sale/sharing scripts until consent state is known | Tag manager admin |
| Confirmation display | Visible acknowledgment that opt-out was processed | Front-end developer |
| Event logging | Timestamped record of consent/opt-out events | Backend or CMP |
Small businesses running WordPress, Shopify, or a custom-built site often lean on a CMP for the banner and confirmation UI, then handle tag gating manually inside their tag manager. That split works fine as long as someone actually tests it end to end, not just at launch, but after every new marketing pixel gets added six months later.
What Your Privacy Policy and Notice at Collection Must Say
Your privacy policy carries most of the legal weight here, more than the banner itself. The CPPA’s guidance on required notices lays out exactly what needs to appear, and skipping any one of these items is an easy, avoidable audit flag.
Your policy needs to disclose:
- The categories of personal information collected, described specifically enough that a visitor understands what’s being gathered.
- The business or commercial purpose for collecting each category.
- The categories of third parties the data is disclosed, sold, or shared with.
- A working “Do Not Sell or Share My Personal Information” link, or the equivalent “Your Privacy Choices” icon link.
- The specific method or methods consumers can use to exercise their rights, along with a note on how you verify request authenticity.
Separately from the privacy policy, you need a “Notice at Collection,” a shorter, contextual disclosure delivered at or before the moment data is actually gathered, not just buried somewhere on the site generally. In practice, most sites handle this through the cookie banner itself, a linked pop-up at signup forms, or a dedicated section near any data-collecting widget like a chat tool or quiz.
A few categories carry extra disclosure requirements: sensitive personal information (things like precise geolocation, health data, or financial account details) needs its own explicit callout, financial incentive programs (discounts in exchange for data) need separate terms explaining the trade, and any site that knowingly collects data from minors needs the opt-in language covered earlier, not the standard opt-out framing.
If you want to see how another small operation structures this kind of disclosure without turning it into a wall of legal text, Finja’s cookie policy breaks categories out clearly while staying readable.
Enforcement Trends: What’s Actually Getting Businesses Fined
Regulators are not chasing hypothetical violations. The California Attorney General’s office has already pursued and settled major CCPA cases tied directly to consent failures, and the pattern in these cases is consistent enough to build a checklist around.
Three failure modes show up again and again in enforcement actions:
- Not honoring GPC signals, either ignoring the header entirely or acknowledging it without actually suppressing the sale/sharing tags behind it.
- Dark-pattern banner design, the asymmetric accept/decline problem covered earlier, which regulators now actively screenshot and cite by name.
- Verification barriers, making it unreasonably difficult for consumers to submit or confirm opt-out requests, sometimes by requiring account creation just to say no to data sharing.
Per-violation penalties under the CCPA can add up fast across a large user base, and the FTC’s coverage of CPPA enforcement guidance makes clear that regulators are treating dark-pattern consent as functionally equivalent to no consent at all, which strips away any defense that a visitor “technically agreed.”
For most small business sites, remediation is straightforward and doesn’t require a legal team on retainer: audit your banner for symmetry, confirm GPC actually suppresses tags rather than just registering them, simplify your opt-out request process so it doesn’t require jumping through account verification hoops, and re-check all of it every time you add a new marketing tool.
Implementation Notes From Moderatemurmurations for US Client Sites
When we build or audit cookie flows for small business clients, we start with the assumption that compliance and conversion don’t have to fight each other, they just need to be designed together instead of bolted on separately.
A footer link that works well in practice reads simply: “Your Privacy Choices” paired with the blue toggle icon, linking to a short page that explains what selling/sharing means for that specific site and gives a one-click opt-out. Pair it with a confirmation line like: “Your opt-out preference has been received and applied.” That single sentence satisfies the visible-confirmation requirement without needing a redesign of the whole banner.
For architecture, we generally recommend:
- A CMP handling the visible banner and storing consumer preference state.
- Server-side detection of the
Sec-GPCheader, so tag suppression happens before the page finishes rendering, not after a script has already fired. - Tag manager rules that gate sale/sharing scripts specifically, while leaving first-party analytics and functional cookies untouched.
Before anything ships, we run through the same short QA pass every time:
- Symmetry test: do accept and decline require the same number of clicks and the same visual prominence?
- GPC browser test: does the opt-out actually apply in Brave and DuckDuckGo, where the signal is on by default?
- No-verification test: can a visitor opt out without creating an account or jumping through identity verification?
Pro Tip: Test your banner from a completely fresh, cleared browser profile, not your own logged-in setup. What you see as the site owner is almost never what a first-time visitor sees, especially once cached preferences are involved.
If your current setup was built years ago and never touched since, this is usually where the gaps show up first.
Balancing Compliance and Conversion: An Editorial Take
Most compliance advice treats consent banners as a legal checkbox, and most conversion advice treats them as friction to minimize. Both framings miss the actual trade-off, which is that a well-designed, symmetrical banner protects you legally and barely dents opt-out rates, while a manipulative one risks both a regulator’s attention and a visitor’s trust in the same click.
That overcorrection costs small businesses real marketing data for no legal reason.
Measure the impact honestly. Track opt-out rates before and after banner changes, and if a symmetrical design barely moves the needle, that tells you the asymmetric version was never doing much for conversion anyway, just quietly building legal risk.
Bring in a specialist when your data flows get genuinely complex, multiple ad networks, cross-device tracking, minors in your audience. A standard CMP handles the basics fine for most small sites.
— Christopher
Get Your Cookie Consent Flow Built Right the First Time
Reading through GPC detection requirements, symmetry rules, and tag-gating logic is one thing. Actually wiring it into a live site without breaking your analytics or your conversion rate is another. This gap can be addressed by working with experts who build cookie consent architecture correctly from the start instead of patching a banner plugin and hoping it holds up.
Services typically begin with a quick site audit: checking the current banner for symmetry issues, testing whether GPC actually suppresses ad tags or just logs the signal, and reviewing footer links and privacy policy language against CPPA requirements. Implementation may then include CMP setup, server-side GPC detection, tag manager gating rules, and confirmation copy, helping ensure the system works effectively.
If your current setup hasn’t been touched since before the 2026 visible-confirmation requirement took effect, now’s the time to check. Book a free consultation with Moderatemurmurations and get a clear read on where your site stands.